HailBytes ASM vs Tenable ASM
A self-hosted EASM alternative for teams that want active recon ownership instead of a passive discovery layer bolted onto a vulnerability-management suite.
TL;DR
Tenable Attack Surface Management (the Bit Discovery acquisition, sold inside Tenable One) is primarily a passive external-asset discovery layer that feeds Tenable’s vulnerability scanners. HailBytes ASM is a self-hosted alternative that owns both discovery and active scanning end-to-end, priced on infrastructure rather than as a Tenable One module.
- Pick HailBytes ASM if you don’t want a Tenable One commitment, need active scan ownership and white-label deliverables, or want unlimited scans at a flat VM cost.
- Stay with Tenable ASM if you’re already standardized on Tenable Vulnerability Management / Nessus and want EASM data piped into the same risk dashboard.
Pricing & Cost Model
| Dimension | HailBytes ASM | Tenable ASM |
|---|---|---|
| Pricing axis | Infrastructure ($0.24/vCPU/hour) | Per asset / per Tenable One subscription tier |
| Annual cost (small surface) | $5,880 (4 vCPU, ASM’s documented minimum; $8,400 list), all-in $8,520 committed and $11,040 at list, below the ~$15,000 Tenable One floor on either basis; this band is a price win at the documented minimum, though 8 vCPU is the size we recommend for production | ~$15,000+ (Tenable One floor) |
| Annual cost (mid surface) | $11,760–$23,520 (8–16 vCPU; $16,800–$33,600 list): a win at 8 vCPU; at 16 vCPU all-in ($40,320 at list) it only just meets the bottom of the Tenable range | $40,000–$100,000+ |
| Standalone purchase | ✅ | 🟡 Typically bundled in Tenable One |
| Free trial | 30 days via AWS / Azure Marketplace | 30-day Tenable One trial |
| Procurement path | Cloud marketplace (counts toward EDP / MACC) | Direct Tenable contract |
HailBytes figures are the 1-year commitment price (delivered as an AWS or Azure private offer, not a discount on the published meter) with list alongside, so the comparison sits on the same annual-contract basis as the competitor column. The meter covers software only; the VM, storage, and networking run in your own cloud account and are billed separately at roughly $35/vCPU/month, $220/month at 4 vCPU, $280 at 8, $560 at 16, and $1,120 at 32, so scale that line to the size on the row you are reading.
Our cost steps with the size of the surface rather than scaling per asset, so every comparison on this page is calculated all-in against the rung that fits. 4 vCPU is ASM’s documented minimum and suits a small, stable surface (about $8,520/year all-in on a 1-year commitment, $11,040 at list). 8 vCPU is the size ASM’s own hardening guide names Production (recommended) and covers 10 to 50 scheduled scans a day ($15,120 / $20,160). 16 vCPU covers 50+ scans a day ($30,240 / $40,320). Quote 4 vCPU only where the surface genuinely is small and stable; 8 vCPU is the size we recommend for production. Full pricing.
Sizing above 8 vCPU: ASM sizes its scan worker from the host, so a larger instance scans proportionally faster: a 16 vCPU deployment gives the scan engine twice the cores an 8 vCPU one does. Instances deployed before August 2026 pick this up on the next update, when the installer rewrites the worker limits to match the machine.
Architecture & Control
| Dimension | HailBytes ASM | Tenable ASM |
|---|---|---|
| Deployment | Self-hosted in your AWS / Azure account | SaaS (Tenable-hosted) |
| Source code access | Ships with the deployment; auditable under NDA | Closed source |
| Data residency | Whatever cloud region you pick | Tenable-controlled regions |
| Custom scan logic / wordlists | ✅ Full control | ❌ |
| Per-tenant isolation | One VM per tenant | Multi-tenant SaaS |
Capability Comparison
| Capability | HailBytes ASM | Tenable ASM |
|---|---|---|
| External asset discovery | ✅ Active recon pipeline | ✅ Passive (Bit Discovery dataset) |
| Active port & service scanning | ✅ Built-in | 🟡 Requires Tenable VM/Nessus pivot |
| CVE matching | ✅ | ✅ (Nessus engine) |
| Vulnerability-management depth | 🟡 OSS toolchain breadth | ✅ Nessus is the mature engine |
| Unlimited scans | ✅ | 🟡 Tier-based |
| Custom wordlists | ✅ Unlimited | ❌ |
| AI-powered analysis | ✅ OpenAI + Ollama (local GPU) | 🟡 ExposureAI (Tenable One add-on) |
| MCP server / AI-agent tooling | ✅ Built-in (Claude / Cursor / Windsurf) | ❌ |
| SIEM integration | ✅ Splunk, Sentinel, Elastic, Chronicle | ✅ Tenable connectors |
| Government cloud (GovCloud / Azure Gov) | ✅ Both | 🟡 Tenable.io for Gov |
| White-label for client deliverables | ✅ Built-in | ❌ |
See It in the Product
Tenable ASM is a SaaS subscription per asset. Below is the self-hosted shape of the same work.
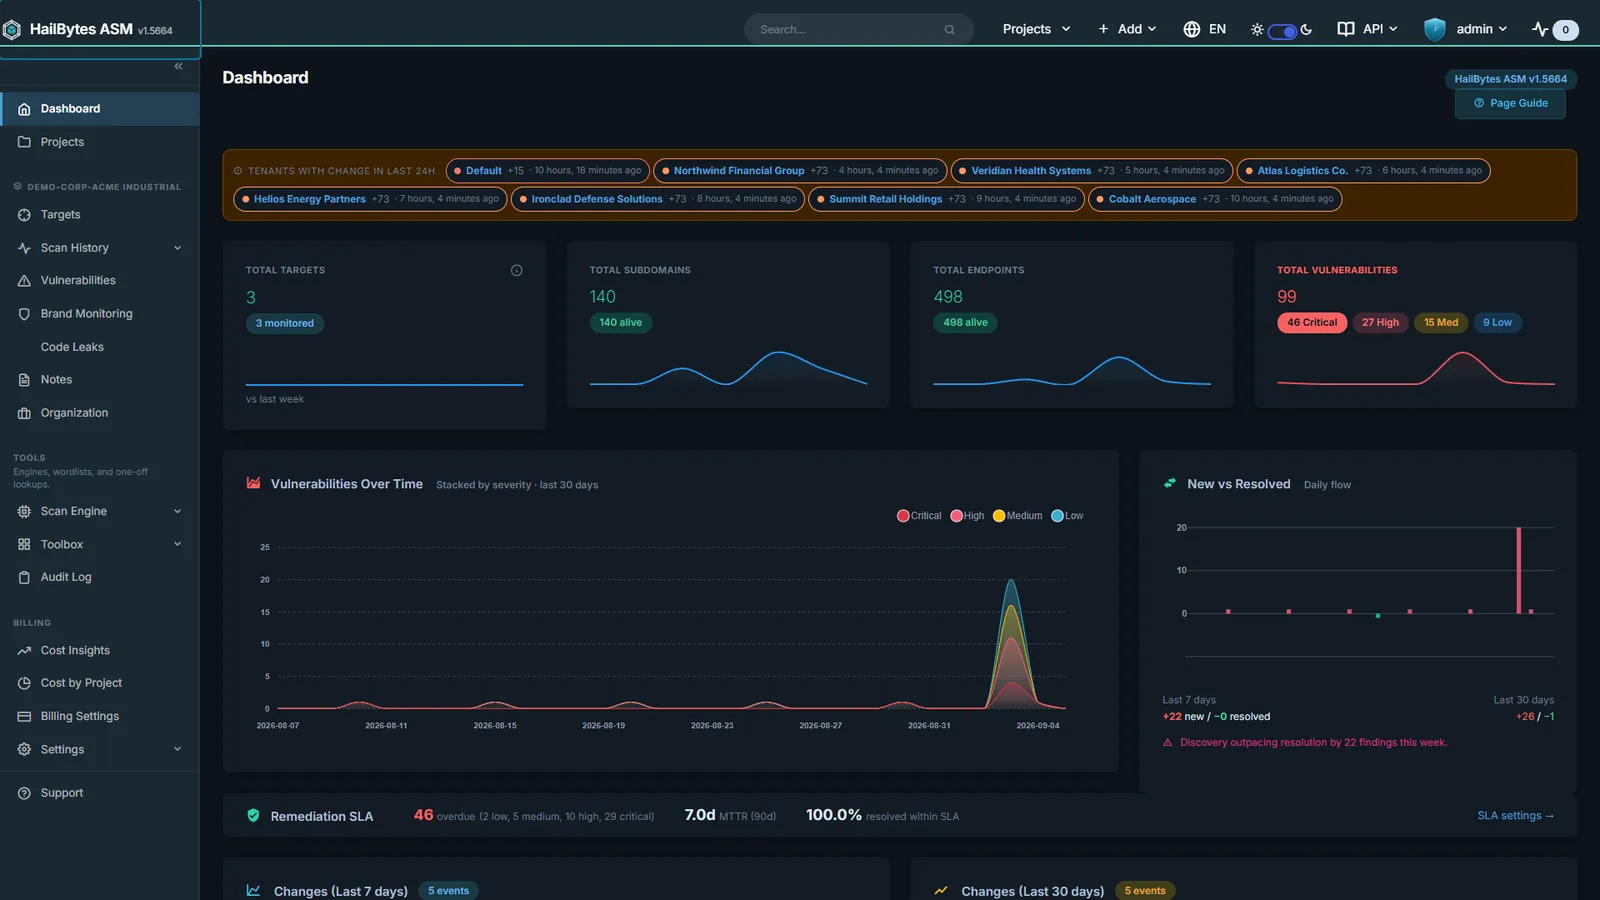
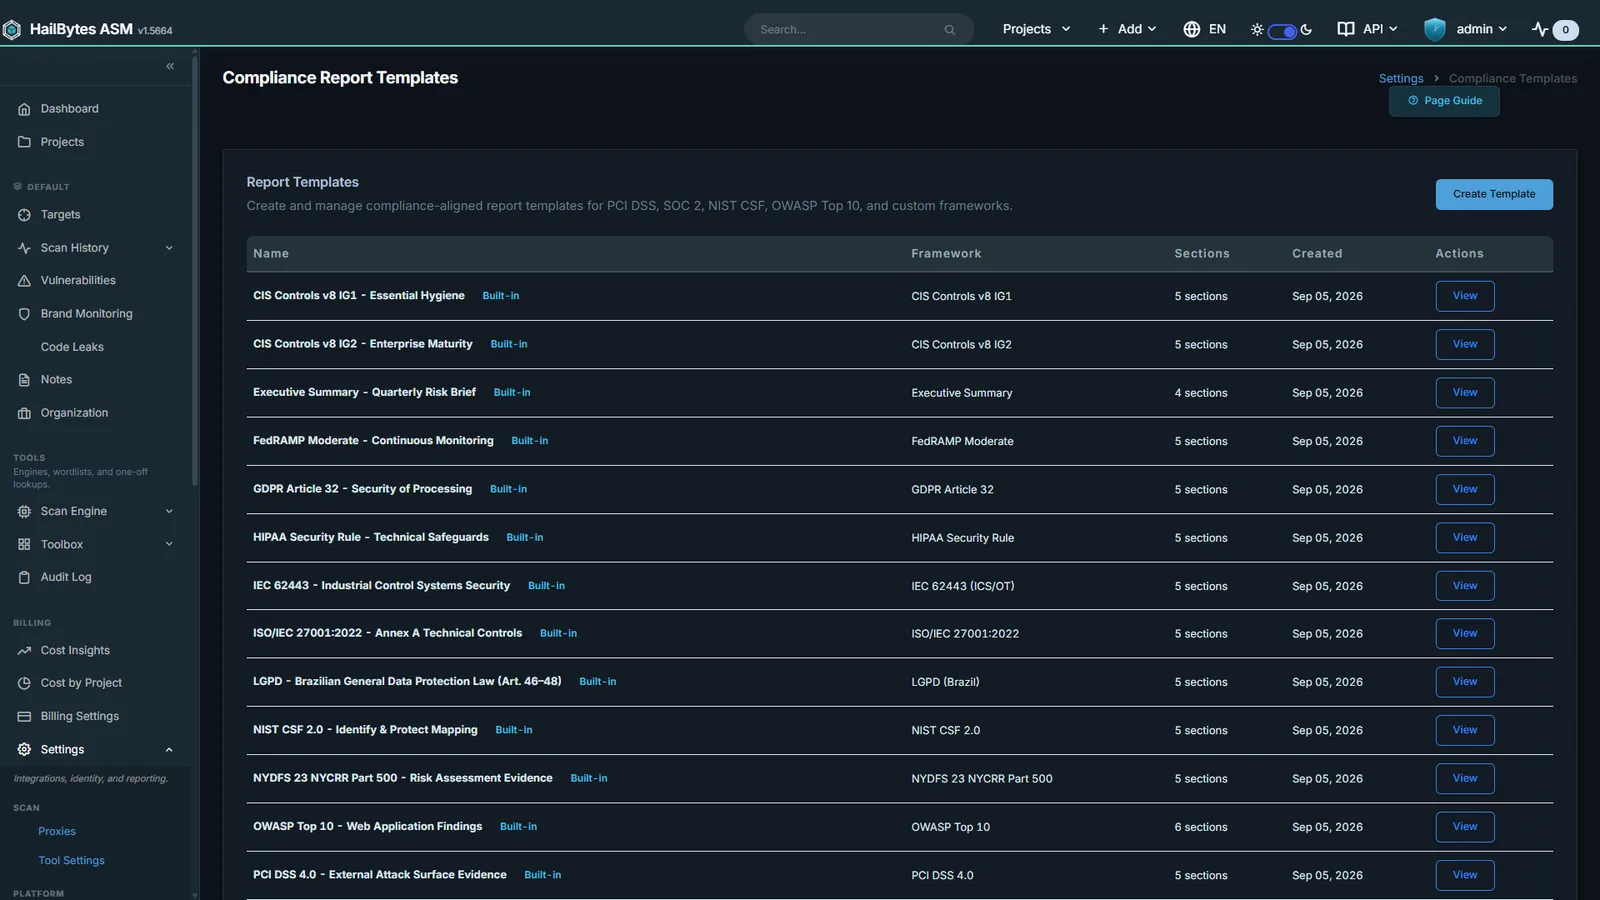
Captured from a running instance. See all 48 screens →
When HailBytes ASM Wins
- You don’t want a Tenable One commitment. Tenable ASM’s value is feeding the broader Tenable VM stack; standalone, the math gets harder.
- MSSPs and pen-test firms. White-label deliverables and per-instance cost make resold continuous monitoring viable. Reselling continuous ASM.
- Active recon ownership. If you want to own the scan pipeline, custom wordlists, and triage logic end-to-end, self-hosting wins.
- AI-agent recon workflows. The built-in MCP server lets Claude, Cursor, and Windsurf drive scans and triage findings.
When Tenable ASM Wins
- Heavy Tenable VM / Nessus shops. Native Tenable One correlation is the real product moat.
- Vulnerability-management depth is the priority. Nessus has decades of detection authoring; pure recon-tooling won’t match that on every CVE class.
- Existing Tenable contract spend that absorbs the ASM SKU at marginal cost.
Try HailBytes ASM
30-day free trial through AWS Marketplace and Azure Marketplace, including the underlying VM.
See HailBytes ASM in Action
Skip the slide deck. Watch the product run end-to-end before you book a call.

Try HailBytes ASM Free
Get a free trial deployment on AWS or Azure. Our team walks you through setup and your first steps, whether that’s a single organization or a multi-client rollout.
- ✓ 30-day free trial on AWS or Azure
- ✓ Guided onboarding from our security team
- ✓ No credit card required to start
- ✓ 40+ security tools pre-configured