HailBytes ASM vs Detectify
A self-hosted Detectify alternative for security teams, MSSPs, and pen-test firms that want continuous external reconnaissance, without per-asset pricing or scan infrastructure controlled by a third party.
TL;DR
Detectify is a SaaS attack-surface monitoring platform with strong web-application vulnerability scanning and a curated finding-quality story. HailBytes ASM is a self-hosted, commercially licensed alternative built on the reNgine reconnaissance engine, priced on infrastructure rather than asset count, and designed for teams that want full ownership of the scan pipeline.
- Pick HailBytes ASM if you have a large or fast-changing attack surface, run an offensive-security firm, want unlimited scans without credit consumption, or need full data sovereignty.
- Stay with Detectify if you primarily care about web-app vulnerability depth (EASM + DAST in one product) and don’t want to manage infrastructure.
Pricing & Cost Model
| Dimension | HailBytes ASM | Detectify |
|---|---|---|
| Pricing axis | Infrastructure ($0.24/vCPU/hour) | Per asset / per domain (tier-based) |
| Annual cost (small surface) | $5,880 (4 vCPU, ASM’s documented minimum; $8,400 list), all-in $8,520 committed and $11,040 at list. Detectify’s cheapest entry tiers still undercut this; we come in below the top of its $15,000 entry band | $5,000–$15,000 |
| Annual cost (mid surface, hundreds of subdomains) | $11,760–$23,520 (8–16 vCPU; $16,800–$33,600 list), clearly below at 8 vCPU, near parity at 16 | $25,000–$60,000+ |
| Annual cost (large surface, thousands of assets) | $23,520–$47,110 (16–32 vCPU; $33,600–$67,300 list): a clear win at 16 vCPU; at 32 vCPU all-in ($80,640 at list) it reaches Detectify’s enterprise floor rather than beating it | $80,000+ (custom enterprise) |
| Free trial | 30 days via AWS / Azure Marketplace | 2 weeks (limited scope) |
| Procurement path | Cloud marketplace (counts toward EDP / MACC) | Direct SaaS contract |
HailBytes figures are the 1-year commitment price (delivered as an AWS or Azure private offer, not a discount on the published meter) with list alongside, so the comparison sits on the same annual-contract basis as the competitor column. The meter covers software only; the VM, storage, and networking run in your own cloud account and are billed separately at roughly $35/vCPU/month, $220/month at 4 vCPU, $280 at 8, $560 at 16, and $1,120 at 32, so scale that line to the size on the row you are reading.
Our cost steps with the size of the surface rather than scaling per asset, so every comparison on this page is calculated all-in against the rung that fits. 4 vCPU is ASM’s documented minimum and suits a small, stable surface (about $8,520/year all-in on a 1-year commitment, $11,040 at list). 8 vCPU is the size ASM’s own hardening guide names Production (recommended) and covers 10 to 50 scheduled scans a day ($15,120 / $20,160). 16 vCPU covers 50+ scans a day ($30,240 / $40,320). Quote 4 vCPU only where the surface genuinely is small and stable; 8 vCPU is the size we recommend for production. Full pricing.
Sizing above 8 vCPU: ASM sizes its scan worker from the host, so a larger instance scans proportionally faster: a 16 vCPU deployment gives the scan engine twice the cores an 8 vCPU one does. Instances deployed before August 2026 pick this up on the next update, when the installer rewrites the worker limits to match the machine.
The gap runs both ways. Below our all-in cost on the 4 vCPU rung, ASM’s documented minimum (about $8,520/year on a 1-year commitment and $11,040 at list), Detectify’s cheapest entry tiers are cheaper; above that the gap widens in HailBytes’s favour, because HailBytes scales on VM size while per-asset pricing scales with asset count.
Architecture & Control
| Dimension | HailBytes ASM | Detectify |
|---|---|---|
| Deployment | Self-hosted in your AWS / Azure account | SaaS (Detectify-hosted) |
| Source code access | Ships with the deployment; auditable under NDA (built on reNgine) | Closed source |
| Data residency | Whatever cloud region you pick | Detectify-controlled regions |
| Scan engine | 40+ open-source recon tools orchestrated | Detectify proprietary + crowdsourced |
| Custom scan logic / wordlists | ✅ Full control | 🟡 Limited |
| Per-tenant isolation | One VM per tenant | Multi-tenant SaaS |
Capability Comparison
| Capability | HailBytes ASM | Detectify |
|---|---|---|
| Subdomain enumeration | ✅ Multi-source (CT logs, brute, passive DNS) | ✅ |
| Port & service scanning | ✅ Full | ✅ |
| CVE matching | ✅ | ✅ |
| Web-app DAST / vuln research | 🟡 OSS-toolchain breadth | ✅ Crowdsourced ethical-hacker depth |
| Unlimited scans | ✅ | ❌ Tier / asset-count limited |
| Custom wordlists | ✅ Unlimited | 🟡 Limited |
| AI-powered analysis | ✅ OpenAI + Ollama (local GPU) | 🟡 Limited |
| MCP server / AI-agent tooling | ✅ Built-in (Claude / Cursor / Windsurf) | ❌ |
| SIEM integration | ✅ Splunk, Sentinel, Elastic, Chronicle | ✅ |
| Jira / Slack routing | ✅ | ✅ |
| Government cloud (GovCloud / Azure Gov) | ✅ Both | 🟡 Limited |
| White-label for client deliverables | ✅ Built-in | ❌ |
See It in the Product
Detectify is strongest on the web-app surface. ASM covers that and the infrastructure either side of it.
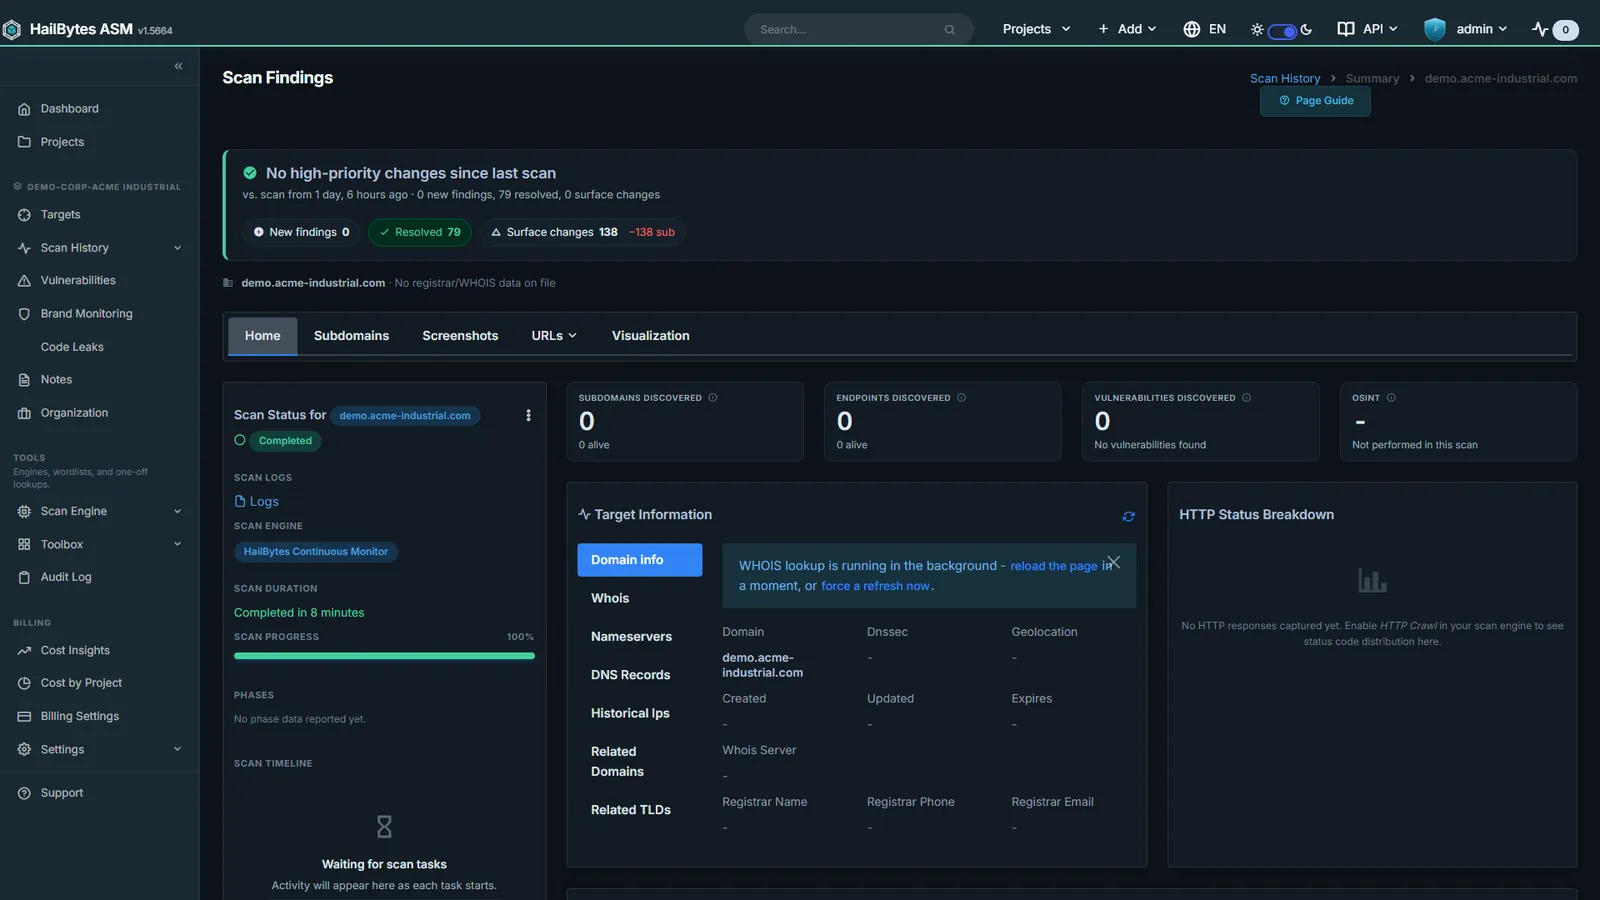
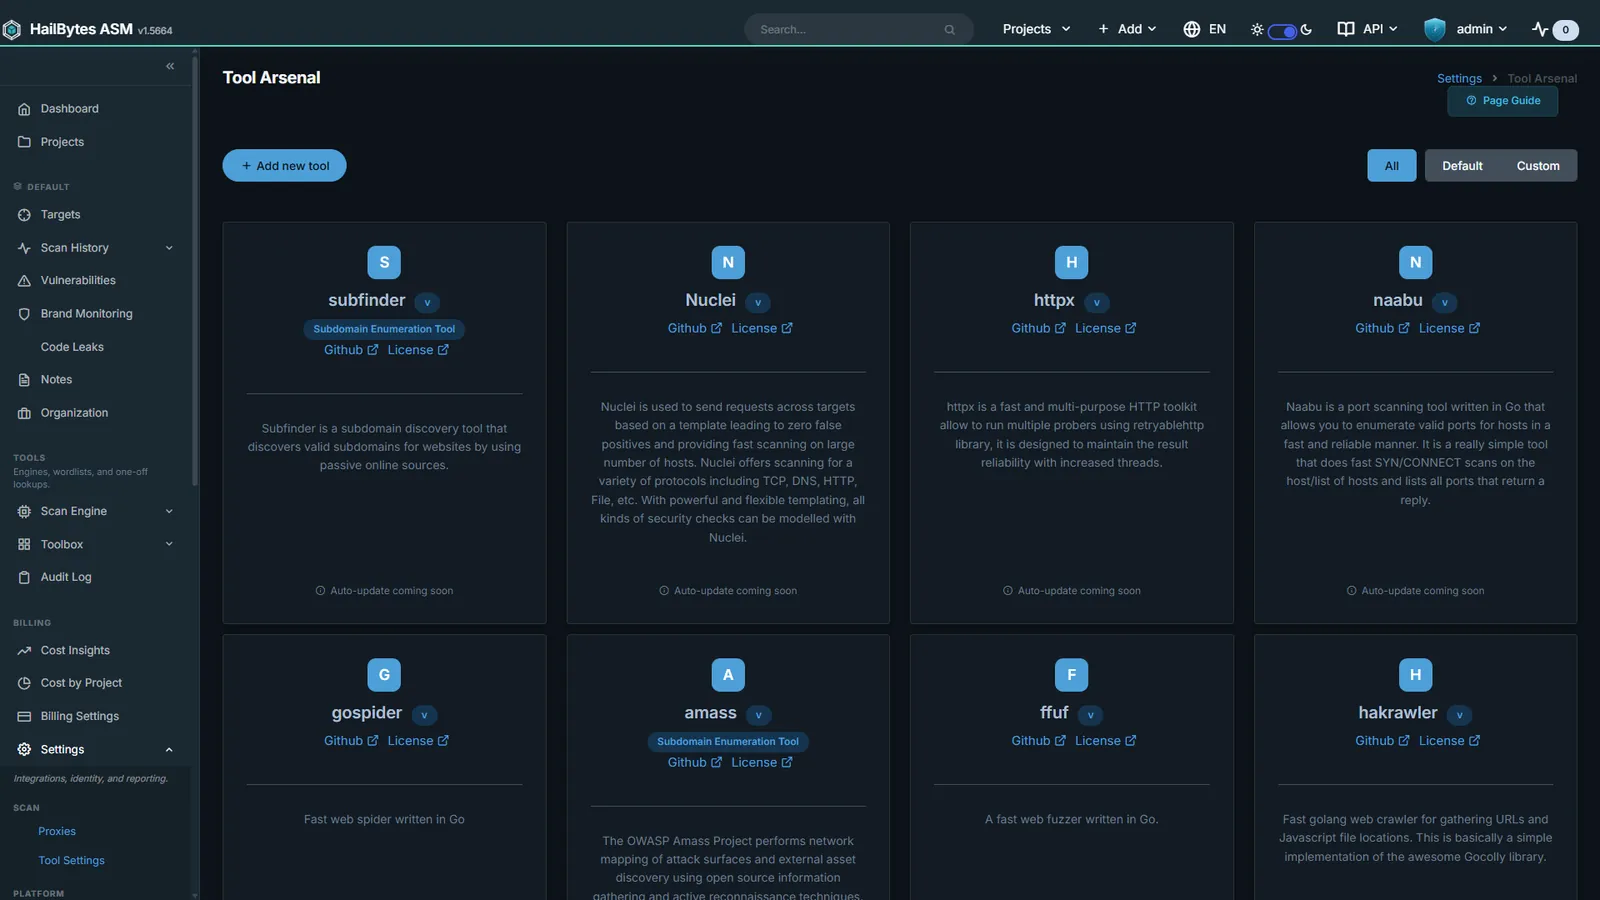
Captured from a running instance. See all 48 screens →
When HailBytes ASM Wins
- Large or fast-growing attack surfaces. Per-asset pricing punishes growth; infrastructure pricing absorbs it. Continuous monitoring blog post.
- Pen-test firms reselling continuous monitoring. Flat per-instance cost is what makes the white-label deliverable pencil out. Pen-test firm playbook.
- Teams that want full source visibility. Auditing your scan pipeline, building custom detection rules, and integrating internal tools all require source access; the HailBytes Commercial License gives it.
- Government and regulated industries. AWS GovCloud and Azure Government deployments keep data inside your own tenancy.
- AI-agent-driven recon workflows. The built-in MCP server lets Claude, Cursor, and Windsurf orchestrate scans, triage findings, and pivot deeper without leaving the IDE.
When Detectify Wins
- Web-application vulnerability depth is your priority. Detectify’s crowdsourced research network produces high-quality web-app findings that pure recon-tooling won’t catch.
- You want EASM and DAST in one product and are willing to pay for the convenience.
- Small, slow-changing attack surfaces. If your asset count is genuinely small and stable, Detectify’s cheapest entry tiers come in under the 4 vCPU rung, ASM’s documented minimum, which all-in, software plus your own cloud bill, is about $8,520/year on a 1-year commitment and $11,040 at list. The top of Detectify’s $15,000 entry band sits above that. That is where the crossover now sits.
Try HailBytes ASM
The AWS and Azure Marketplace listings include a 30-day free trial covering the underlying VM. Run it against your own attack surface alongside your Detectify deployment and compare findings, scan cadence, and triage workflow side by side.
Related Comparisons
Other external attack-surface and recon platforms usually evaluated alongside Detectify:
- vs Censys: internet-wide certificate and port intelligence.
- vs Shodan: the original device search engine.
- vs Microsoft Defender EASM: Azure-native external ASM.
- vs runZero: asset inventory and network discovery.
- Full ASM comparison matrix: every vendor side by side, plus the HailBytes ASM product page.
See HailBytes ASM in Action
Skip the slide deck. Watch the product run end-to-end before you book a call.

Try HailBytes ASM Free
Get a free trial deployment on AWS or Azure. Our team walks you through setup and your first steps, whether that’s a single organization or a multi-client rollout.
- ✓ 30-day free trial on AWS or Azure
- ✓ Guided onboarding from our security team
- ✓ No credit card required to start
- ✓ 40+ security tools pre-configured